An AI-generated pull request changes a payment route, an SVG icon, and a dependency lockfile. GitHub Copilot leaves a review with no warnings. Is it safe to merge? Not yet: a clean comment does not mean every file was analyzed. GitHub's November 6 update makes coverage and review context easier to inspect, which is exactly what a solo builder needs before accepting code produced quickly.
In its November 6, 2026 changelog, GitHub introduced a more compact review overview. Skipped and excluded files now share a Files not reviewed section with filenames and linked reasons. The overview also shows the review effort used and, when reported, which skills, MCP servers, or custom instructions informed a comment. REST and GraphQL attribution fields were added for teams that audit reviews programmatically, but you do not need to call an API to use the new overview on a PR.
“No findings” is not the same as “covered”
GitHub documents file types excluded from Copilot code review, including some dependency files, logs, SVGs, and generated or vendor code. If a change touches an icon or lockfile, a missing Copilot comment about that file has always been ambiguous. The new unreviewed-files section turns that ambiguity into a list you can act on.
It does not prove that reviewed files are correct. GitHub itself says Copilot review does not replace human review. A later review may also collapse older findings unrelated to the latest push; do not mistake a short overview for the entire PR history.
Run a small PR exercise
- Open a test PR that changes one function and, if relevant, an SVG or lockfile. Request Copilot under Reviewers. GitHub's official guide covers the request and re-review flow.
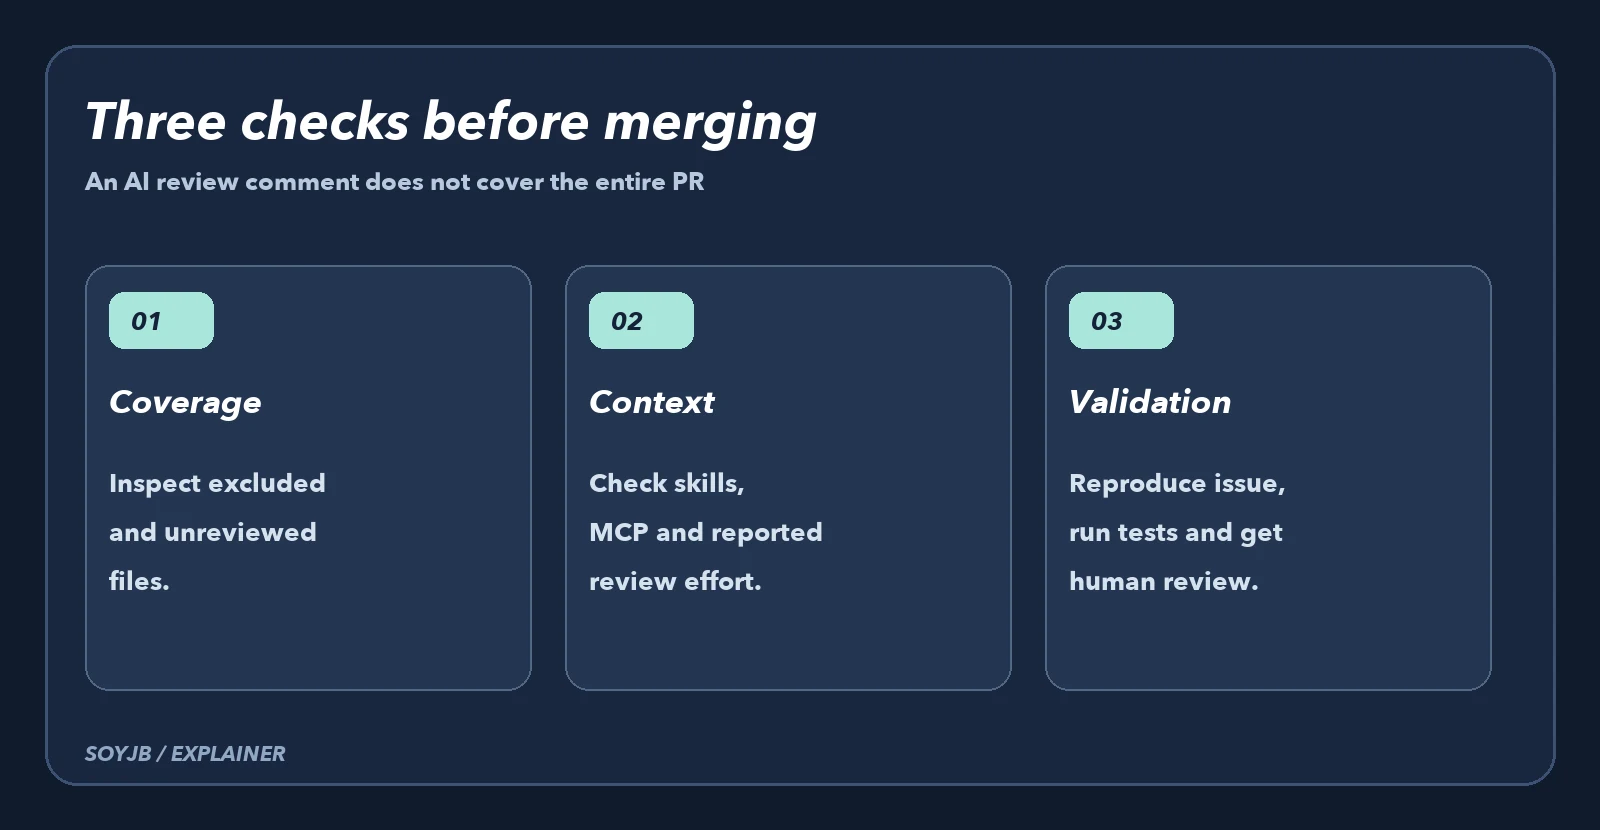
- When the overview appears, open Files not reviewed. Compare its list with Files changed. Assign a human check to each skipped file: inspect the icon, validate dependencies, or test the related behavior.
- Read the effort level and context attributions if available. If you expected a repository skill or MCP server to supply review rules and it is absent, do not assume it was used. Check the configuration and linked session when available.
- Reproduce important findings, run tests, and ask a person to review permissions, data handling, and product tradeoffs. After pushing changes, request a re-review or enable reviews on new pushes; a manually requested review does not automatically rerun by default.
This is an editorial test plan, not a PR that SoyJB ran. A useful output is a simple table: file, Copilot coverage, human check, evidence, and decision. For changes to authentication, payments, or personal data, pair that table with end-to-end tests and a named owner.
Access and limits
GitHub lists this update for Copilot Pro, Pro+, Max, Business, and Enterprise. Balanced or Max effort can consume more credits, according to its configuration guide, so do not turn maximum effort on for every PR without a reason. The overview and attributions report what Copilot analyzed or says it used. They do not certify complete coverage or correctness. Tests, human review, and business context still determine whether a change should ship.
Sources: GitHub announcement, Nov 6, 2026; excluded files; code review guide. Reviewed Nov 7, 2026.